Yes, you can migrate most websites with zero visible downtime. The method: build the new host in parallel, lower your DNS TTL days ahead, run a final delta sync while briefly pausing writes, flip DNS, then monitor. The one exception is a very large or write-heavy site, where replication or blue-green traffic shifting replaces the simple sync-and-flip approach.
TL;DR:
- Lowering DNS TTL to around 300 seconds at least 48 hours before cutover enables near-instant DNS propagation during migration.
- Use rsync for incremental file transfers and plan a short write-freeze to prevent data drift, especially for sites with active uploads or edits.
- Test the new host privately via hosts-file overrides to verify site functionality, SSL, and third-party integrations before public DNS flip.
- Update CDN origin IPs directly and purge caches immediately after switch to ensure visitors see fresh content from the new server.
- Keep the old host running for at least 48 to 72 hours post-migration, monitor traffic, and revert DNS if critical errors occur during propagation.
Table of Contents
- Migrate a Website Without Downtime: The Prep Work That Makes It Possible
- Copying Files and Databases Without Losing Data
- How Do You Test a New Host Before Going Live?
- What Is the Exact Cutover Sequence for a Zero-Downtime Migration?
- How Do You Protect SEO Rankings During a Website Migration?
- What Should You Monitor After the DNS Flip?
- How Denver County Web Design Handles Migrations for Contractor Sites
- How Do You Keep Users Logged In During Cutover?
- What Happens to Your CDN and Cache During Migration?
- How Do You Communicate a Migration to Your Users?
- How Do You Handle Email During a Website Migration?
- What the Textbook Migration Guides Get Wrong
- Get a Managed Migration for Your Contractor Website
- Key Resources for a Zero-Downtime Migration
- Sources
- FAQ
Migrate a Website Without Downtime: The Prep Work That Makes It Possible
Most failed migrations don’t fail on cutover day. They fail two weeks earlier, when someone skipped the inventory step and forgot the site has three cron jobs and a payment webhook nobody documented. Preparation is where you buy yourself the right to be calm on launch day.
Start with a full inventory of everything that has to move:
- Application code and themes/plugins (or your framework’s equivalent)
- Media files and uploads directories
- Databases, including any secondary databases for caching or search
- Cron jobs and scheduled tasks
- DNS records: A, AAAA, CNAME, MX, TXT, and any SPF/DKIM entries
- API keys, whitelisted IPs, and third-party service connections (payment gateways, email providers, CRM webhooks)
Once you know what’s moving, match the environment. The new host needs the same PHP or runtime version, the same database engine and version, and the same extensions the old one relies on. Mismatched versions are the number one cause of “it worked on staging but broke in production.” Get your SSL certificate issued or ready to activate on the new host before you need it, not after.
Then handle DNS timing, which is the step most guides rush past. Lower your DNS TTL to around 300 seconds at least 48 hours before your planned cutover, and let the old TTL fully expire before moving forward. This single step is what makes near-instant propagation possible later, according to zero-downtime migration guidance from MassiveGRID.
Finally, document access credentials, take full backups of files and databases, and write an explicit rollback plan with clear triggers (“if error rate exceeds X, revert DNS”). If you’re not entirely sure who controls your domain registrar login or hosting account, resolve that before migration day, not during it.
Pro Tip: Set a calendar reminder for the moment your old TTL expires, not just the moment you lower it. Migrating before the old TTL clears means some visitors are still getting cached DNS answers pointing at the old server.
Copying Files and Databases Without Losing Data
File transfers and database syncing are where most of the actual migration work happens, and where sloppy tooling creates the data loss that scares people away from zero-downtime approaches in the first place.
For files, rsync over SSH is the standard tool because it only transfers what has changed, which matters enormously once you’ve done the initial full copy. Run that first full copy several days before cutover, then schedule incremental rsyncs to catch new uploads and edits as they happen. Rsync can even run as a recurring cron job, keeping the delta small right up to launch, a pattern outlined in HostDir’s zero-downtime migration playbook. If you’d rather work through a graphical interface than the command line, a tool like FileZilla handles manual FTP/SFTP transfers reasonably well for smaller sites.
For media-heavy sites, consider a shortcut: point both the old and new host at the same shared object storage bucket. That eliminates file syncing entirely for uploads, since both environments read from the same source.
Database handling depends on your platform and traffic pattern:
- WordPress sites can use WP-CLI to script database exports, imports, and safe search-and-replace of URLs, which removes a lot of manual error from the process, per WP-CLI’s documented database commands.
- Watch the
--regexflag on search-replace operations. It’s powerful but easy to misfire on, so test it against a staging copy first. - Busier, transactional sites should look at MySQL replication or binlog streaming instead of a single dump and import.
- Lower-traffic sites can usually get away with a dump, an import, and one final delta sync.
Whatever your setup, plan a short write-freeze right before that final sync. Pausing writes for a few minutes, even on a checkout flow, is what prevents “database drift,” where new orders or form submissions land on the old server after your last sync already ran, a risk IBM’s migration guidance calls out directly.
Pro Tip: If pausing writes isn’t an option for your business, don’t force it. Route new writes through a queue or replicate them to both databases temporarily instead of gambling on a clean freeze window.
How Do You Test a New Host Before Going Live?
Test it privately, using the real domain name, before you ever touch public DNS. This is the step that catches the problems that only show up when the site thinks it’s actually itself, and it’s non-negotiable.
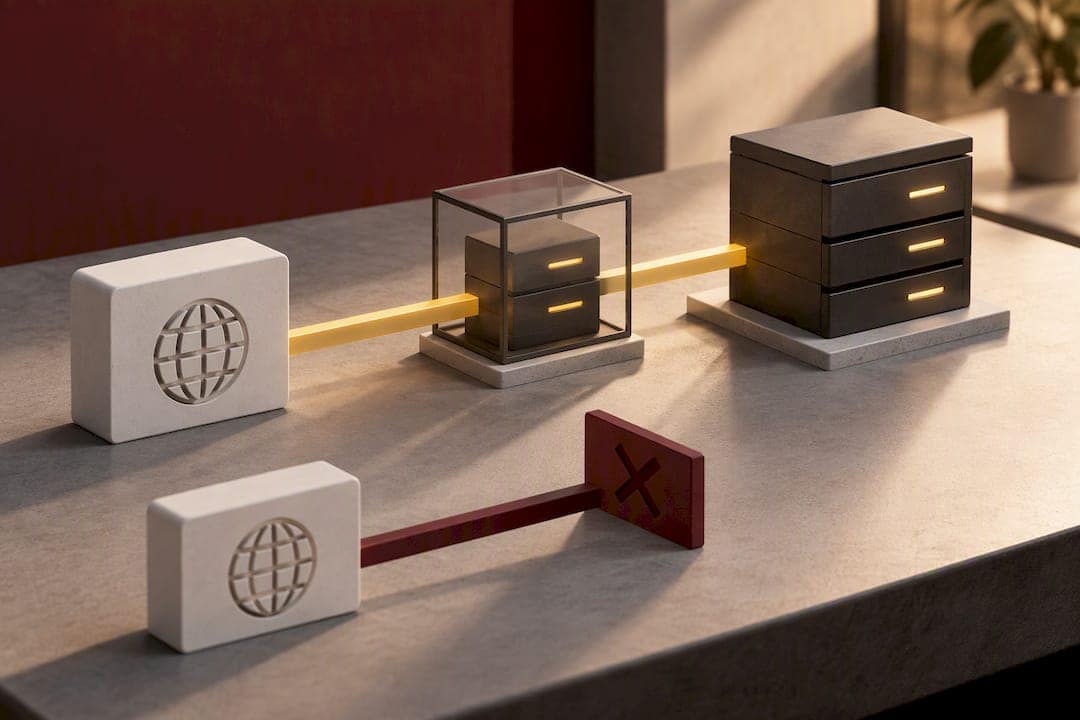
The standard method is a hosts-file override: you edit your own machine’s hosts file to point the domain at the new server’s IP address, then browse the site normally in your browser. Because you’re hitting the real hostname, permalinks, canonical tags, and cookies behave exactly as they will after cutover, unlike testing on a raw staging URL, which LaunchPad Host’s migration guide recommends as the reliable way to catch hostname-dependent bugs.
Once you can see the real site on the new server, work through a smoke test checklist:
- Log in as an admin and as a regular user
- Submit every form on the site, including contact and quote requests
- Run a full checkout or lead-capture flow if the site sells anything or generates leads
- Upload a file if your site accepts uploads
- Confirm cron jobs and scheduled tasks actually fire on the new server
- Check that email sending, payment gateways, and any other third-party integrations connect correctly
Along the way, verify the SSL certificate is valid and trusted, and that every internal link and media asset loads over HTTPS without mixed-content warnings.
Don’t treat this as a solo checkbox exercise. Get explicit sign-off from whoever owns the business outcome, whether that’s a marketing lead worried about lead forms or an owner worried about the online booking calendar, before you schedule the cutover window.
What Is the Exact Cutover Sequence for a Zero-Downtime Migration?
Cutover day has a fixed order, and skipping steps out of impatience is how “zero downtime” migrations turn into three-hour outages.
- Run the final delta sync of files, catching anything created since your last incremental rsync.
- Perform the final database export and import, or let replication catch up if you’re using that method.
- If you can’t avoid a short write-freeze, put the old site into read-only mode for that window.
- Update your A and AAAA records (and any CNAME entries) to point at the new host’s IP address.
- If the site sits behind a proxy or CDN like Cloudflare, changing the origin IP there instead of waiting on public DNS can speed up the effective cutover.
- Watch access and error logs on both the old and new servers simultaneously as traffic starts to shift.
Because you lowered TTL to roughly 300 seconds days earlier, most resolvers should pick up the new IP within minutes rather than the 24 to 48 hours a default TTL would cause, according to MassiveGRID’s zero-downtime migration research. That’s the entire point of the TTL prep work from earlier.
Keep the old host running and untouched through the propagation window. Some visitors, especially on networks with aggressive DNS caching, will still hit the old server for a short while, and you want that experience to work correctly rather than erroring out.
If you see a spike in 500 errors, broken checkout flows, or missing assets right after the flip, revert DNS back to the old host using the rollback plan you wrote during prep. A fast revert beats a slow, panicked fix every time.
Pro Tip: Prefer updating individual A and CNAME records within your existing DNS provider rather than switching nameservers entirely. Nameserver changes propagate far slower and give you much less control over timing.
How Do You Protect SEO Rankings During a Website Migration?
Rankings drop when redirects are missing, sitemaps go stale, or tracking silently breaks, and none of that requires a DNS problem to happen.
Before cutover, crawl your existing site and build a complete map of every live URL. From that map, build a 301 redirect plan for any URL that’s changing, because a documented URL map and redirect plan is what SEO analysts consistently point to as the difference between a migration that holds rankings and one that tanks them, per SEMrush’s website migration checklist. If your URL structure is changing as part of this move, it’s worth reviewing safe URL restructuring practices before you finalize the redirect map, since bad slug decisions compound with migration risk.
After cutover, work through this checklist:
- Test that every redirect returns a 200 status at its target, with no chains of three or four hops in a row.
- Remove any
noindextag that was applied to the staging environment. This single oversight has quietly killed more migrations than any DNS mistake. - Submit a fresh XML sitemap to Google Search Console and request re-crawling of key pages.
- Confirm GA4 conversion events and any ad pixels are still firing correctly on the new host, since a moved script tag or missing container ID will silently zero out your conversion data.
Then put a date on the calendar 30 days out for a full SEO audit. Compare rankings, impressions, and conversion numbers against your pre-migration benchmarks. Small dips in the first week are normal. A sustained drop past 30 days usually points to a redirect or indexing issue that needs fixing, not a Google penalty.
What Should You Monitor After the DNS Flip?
The migration isn’t finished the moment DNS flips. It’s finished when you’ve confirmed traffic, data, and search visibility are all stable on the new host.
- Use a global DNS propagation checker to confirm the new IP is resolving consistently across regions.
- Watch server logs on both hosts. Traffic should shift steadily to the new server and taper off on the old one.
- Keep the old host running for 48 to 72 hours minimum, longer if your original TTL was high or your audience is spread globally.
- Reconcile any writes, orders, or form submissions that landed on the old server during the transition window.
- Once traffic has fully stabilized, restore normal DNS TTL values, confirm SSL auto-renewal is configured, and verify backups and monitoring are active on the new environment.
- Run a fresh crawl to catch any 404s or redirect chains that slipped through, and fix them before they show up in Search Console.
How Denver County Web Design Handles Migrations for Contractor Sites
Migrations for home service businesses carry extra weight because a broken contact form during the switch means a lost job, not just a bad afternoon. Migrations often build around checklist-driven staging, ownership handoffs, and redirect mapping to prevent interruptions in lead flow.
- Non-technical owners juggling day-to-day operations benefit most from a managed migration.
- Sites with active Google Ads campaigns or complex booking integrations carry higher risk if something breaks mid-move.
- High-value lead funnels are worth protecting with professional oversight rather than a DIY attempt.
How Do You Keep Users Logged In During Cutover?
Nothing frustrates a returning customer faster than getting bounced out of their account mid-session because a migration broke their login. Session persistence takes deliberate handling, not luck.
If your application stores sessions in the database rather than on local disk, you’re in good shape already, since your final delta sync carries session data over along with everything else. The risk shows up when sessions are stored in server-local files or in-memory caches like a local Redis instance that doesn’t get migrated alongside the database. In that case, active sessions on the old server simply vanish for anyone who’s logged in when you flip DNS.
The safer pattern is externalizing session storage before migration day, moving to a shared Redis or database-backed session store both old and new servers can read from during the transition window. If that’s not feasible on your timeline, expect some logged-in users to get logged out and plan your cutover for low-traffic hours to limit how many people that affects.
Shopping carts and in-progress form data deserve the same attention. If your cart state lives in a database table, it survives the move cleanly. If it’s stored in browser-side cookies tied to a session ID that changes, test that flow specifically during your private smoke test, not after launch. Users mid-checkout during a cutover window are exactly the people you can’t afford to lose.
What Happens to Your CDN and Cache During Migration?
A content delivery network that’s still serving cached pages from your old server’s IP will quietly undo everything you just accomplished. CDN and cache handling needs its own line item in your runbook, separate from the DNS flip itself.
If you run a CDN or proxy like Cloudflare in front of your site, update the origin IP there directly rather than waiting for public DNS to catch up everywhere. That’s often the fastest single lever you have on cutover day, since the CDN edge nodes start pulling from the new origin immediately once you make the change.
Cached pages are the other half of the problem. Any full-page cache, whether it’s at the CDN layer, a plugin-level cache, or a reverse proxy like Varnish, needs a deliberate purge after cutover, or visitors will keep seeing stale content served from edge locations that haven’t refreshed yet. Purge the CDN cache immediately after switching the origin, then spot-check a handful of pages from different geographic regions to confirm they’re pulling fresh content from the new server.
Don’t forget browser-level caching either. If any assets changed paths or filenames during the migration, check your cache-control headers so returning visitors aren’t stuck loading a broken stylesheet from a cached HTML page that references the old asset structure.
How Do You Communicate a Migration to Your Users?
Silence is the wrong communication strategy for a migration, even a perfectly executed one, because a support inbox full of “is your site down?” messages is an unforced error.
For most business sites, a short heads-up is enough: a banner or email a few days ahead noting that some site improvements are coming and brief hiccups are possible during a specific window. Pick a low-traffic time for that window, communicate it clearly, and you’ll rarely hear from anyone at all. For sites with logged-in users, mention that they might occasionally need to log back in during the transition, so it reads as expected rather than alarming.
If your business runs any kind of status page or has an active social presence, a brief note there covers customers who check before reaching out. The goal isn’t drama. It’s simply making sure that if something does look off for a few minutes, your users already have context instead of assuming the business itself is in trouble.
How Do You Handle Email During a Website Migration?
Email is easy to overlook because it often runs on completely separate infrastructure from your website, and that separation is exactly what protects you here.
If your email is hosted through Google Workspace, Microsoft 365, or a dedicated email provider rather than through your web host, your MX records aren’t changing at all during this migration. Leave them alone. The only DNS records you’re touching are the A, AAAA, and CNAME records tied to your website itself, not the MX, SPF, or DKIM entries that route your mail.
The risk only appears if your web host also handles your email inboxes, which is common with smaller shared hosting setups. In that case, treat email as its own migration project running in parallel, with its own careful sequencing, rather than assuming it will just follow the website over automatically. Migrating mailboxes has its own data integrity risks, and mixing that timeline with your website cutover multiplies the chances something goes wrong on both fronts at once.
Either way, confirm your SPF, DKIM, and DMARC records are intact and correctly pointing wherever your mail actually originates, since a misconfigured SPF record after a DNS cleanup is a quiet, common way for legitimate emails to start landing in spam folders right after a migration.
What the Textbook Migration Guides Get Wrong
Most migration guides treat this as a purely technical exercise: sync the files, flip the DNS, done. That framing misses where migrations actually go wrong for the site owners and admins doing this in practice, which is almost never the DNS step itself.
The standard playbook of prepare, replicate, test, cut over, and finalize works well for the overwhelming majority of business sites, and that includes most contractor and service-business websites. Where it breaks down is with very high-traffic or write-heavy sites, which genuinely need blue-green deployments or load-balancer traffic shifting instead of a simple sync-and-flip. If you’re running an e-commerce platform doing thousands of transactions an hour, this guide’s approach needs real replication infrastructure behind it, not just a longer write-freeze.
For everyone else, the actual failure point is discipline, not technique. Skipping the hosts-file smoke test because “it looked fine on staging” is the single most common cause of a bad cutover I’ve seen described across migration postmortems. The TTL step gets skipped too, because it requires patience two days before a deadline, which is exactly when patience runs out. Prioritize the boring steps: TTL timing, the private smoke test, and a written rollback trigger. The exciting part, the DNS flip itself, is the easy part if everything before it was done right.
— Luis
Get a Managed Migration for Your Contractor Website
Running through checklists across DNS, databases, and redirect maps is manageable once. Doing it right while also running a plumbing, electrical, or landscaping business is a different problem entirely, and that’s the gap Denver County Web Design closes for contractor site owners across Colorado. Rather than handing you a generic hosting company’s migration ticket queue, the staging, final sync, and SEO safeguards described throughout this guide can be included as part of a managed migration project, allowing clients to maintain full ownership of their finished site without recurring monthly fees.
If your site needs to move hosts, or you’re overdue for a redesign that includes a clean migration as part of the build, the next step is simple: get a site audit and migration estimate. Denver County Web Design will look at your current setup, flag anything that raises cutover risk (old plugins, missing SSL, tangled DNS), and give you a realistic timeline before any work starts. Start by reviewing the WordPress Web Design options if a redesign is on the table, or check the full services lineup to find the right fit for your business and get a timeline started this week.
Key Resources for a Zero-Downtime Migration
Keep these on hand while you plan your cutover:
- WP-CLI database commands for scripted WordPress database migrations
- FileZilla for manual FTP/SFTP file transfers
- SEMrush’s migration checklist for redirect and URL mapping
- Real Connected for post-migration conversion tracking audits
Sources
FAQ
How Do You Migrate Data Without Downtime?
You copy data in stages: an initial full transfer, followed by incremental syncs that catch changes, ending with a final delta sync right before cutover. For databases, a brief write-freeze during that last sync prevents new records from being lost, a step IBM’s migration guidance identifies as the key defense against data drift.
How Do You Migrate a Website Without Losing SEO Rankings?
Map every existing URL and build a 301 redirect plan before you touch anything, since missing redirects are the top cause of ranking loss during migrations, according to SEMrush’s website migration checklist. After cutover, remove any leftover noindex tags, submit a fresh sitemap to Google Search Console, and audit rankings again after 30 days.
What Is Zero-Downtime Migration?
Zero-downtime migration means moving a website to a new host or environment so visitors never see an outage or broken page during the switch. It relies on running the old and new environments in parallel, lowering DNS TTL in advance, and only flipping traffic once the new host has been fully tested and verified.
How Long Does It Take to Migrate a Website?
For most business sites, the technical cutover itself takes minutes once DNS propagates, thanks to a lowered TTL, but the full process, including prep, testing, and the 30 day SEO audit, spans several weeks. Denver County Web Design typically builds migration timelines into a broader website redesign project so testing and launch are coordinated rather than rushed.
Do I Need a Developer to Migrate My Site Safely?
Technically confident owners can follow this runbook using rsync, WP-CLI, and a hosts-file smoke test on their own. Sites with active ad campaigns, complex integrations, or owners who’d rather not touch DNS records directly are usually better served by a managed migration handled by a team that does this routinely.